Bitlog WMS for IT

A cloud-native, API-first WMS that's honest about its AI

Your warehouse team wants a new WMS. Before you sign off, you need straight answers on the architecture: is it really cloud-native, is our data isolated, will it stay up, will it connect to what we already run, and where is the AI actually real. Here they are, sourced from Bitlog's Security, Resilience and Operations Brief.
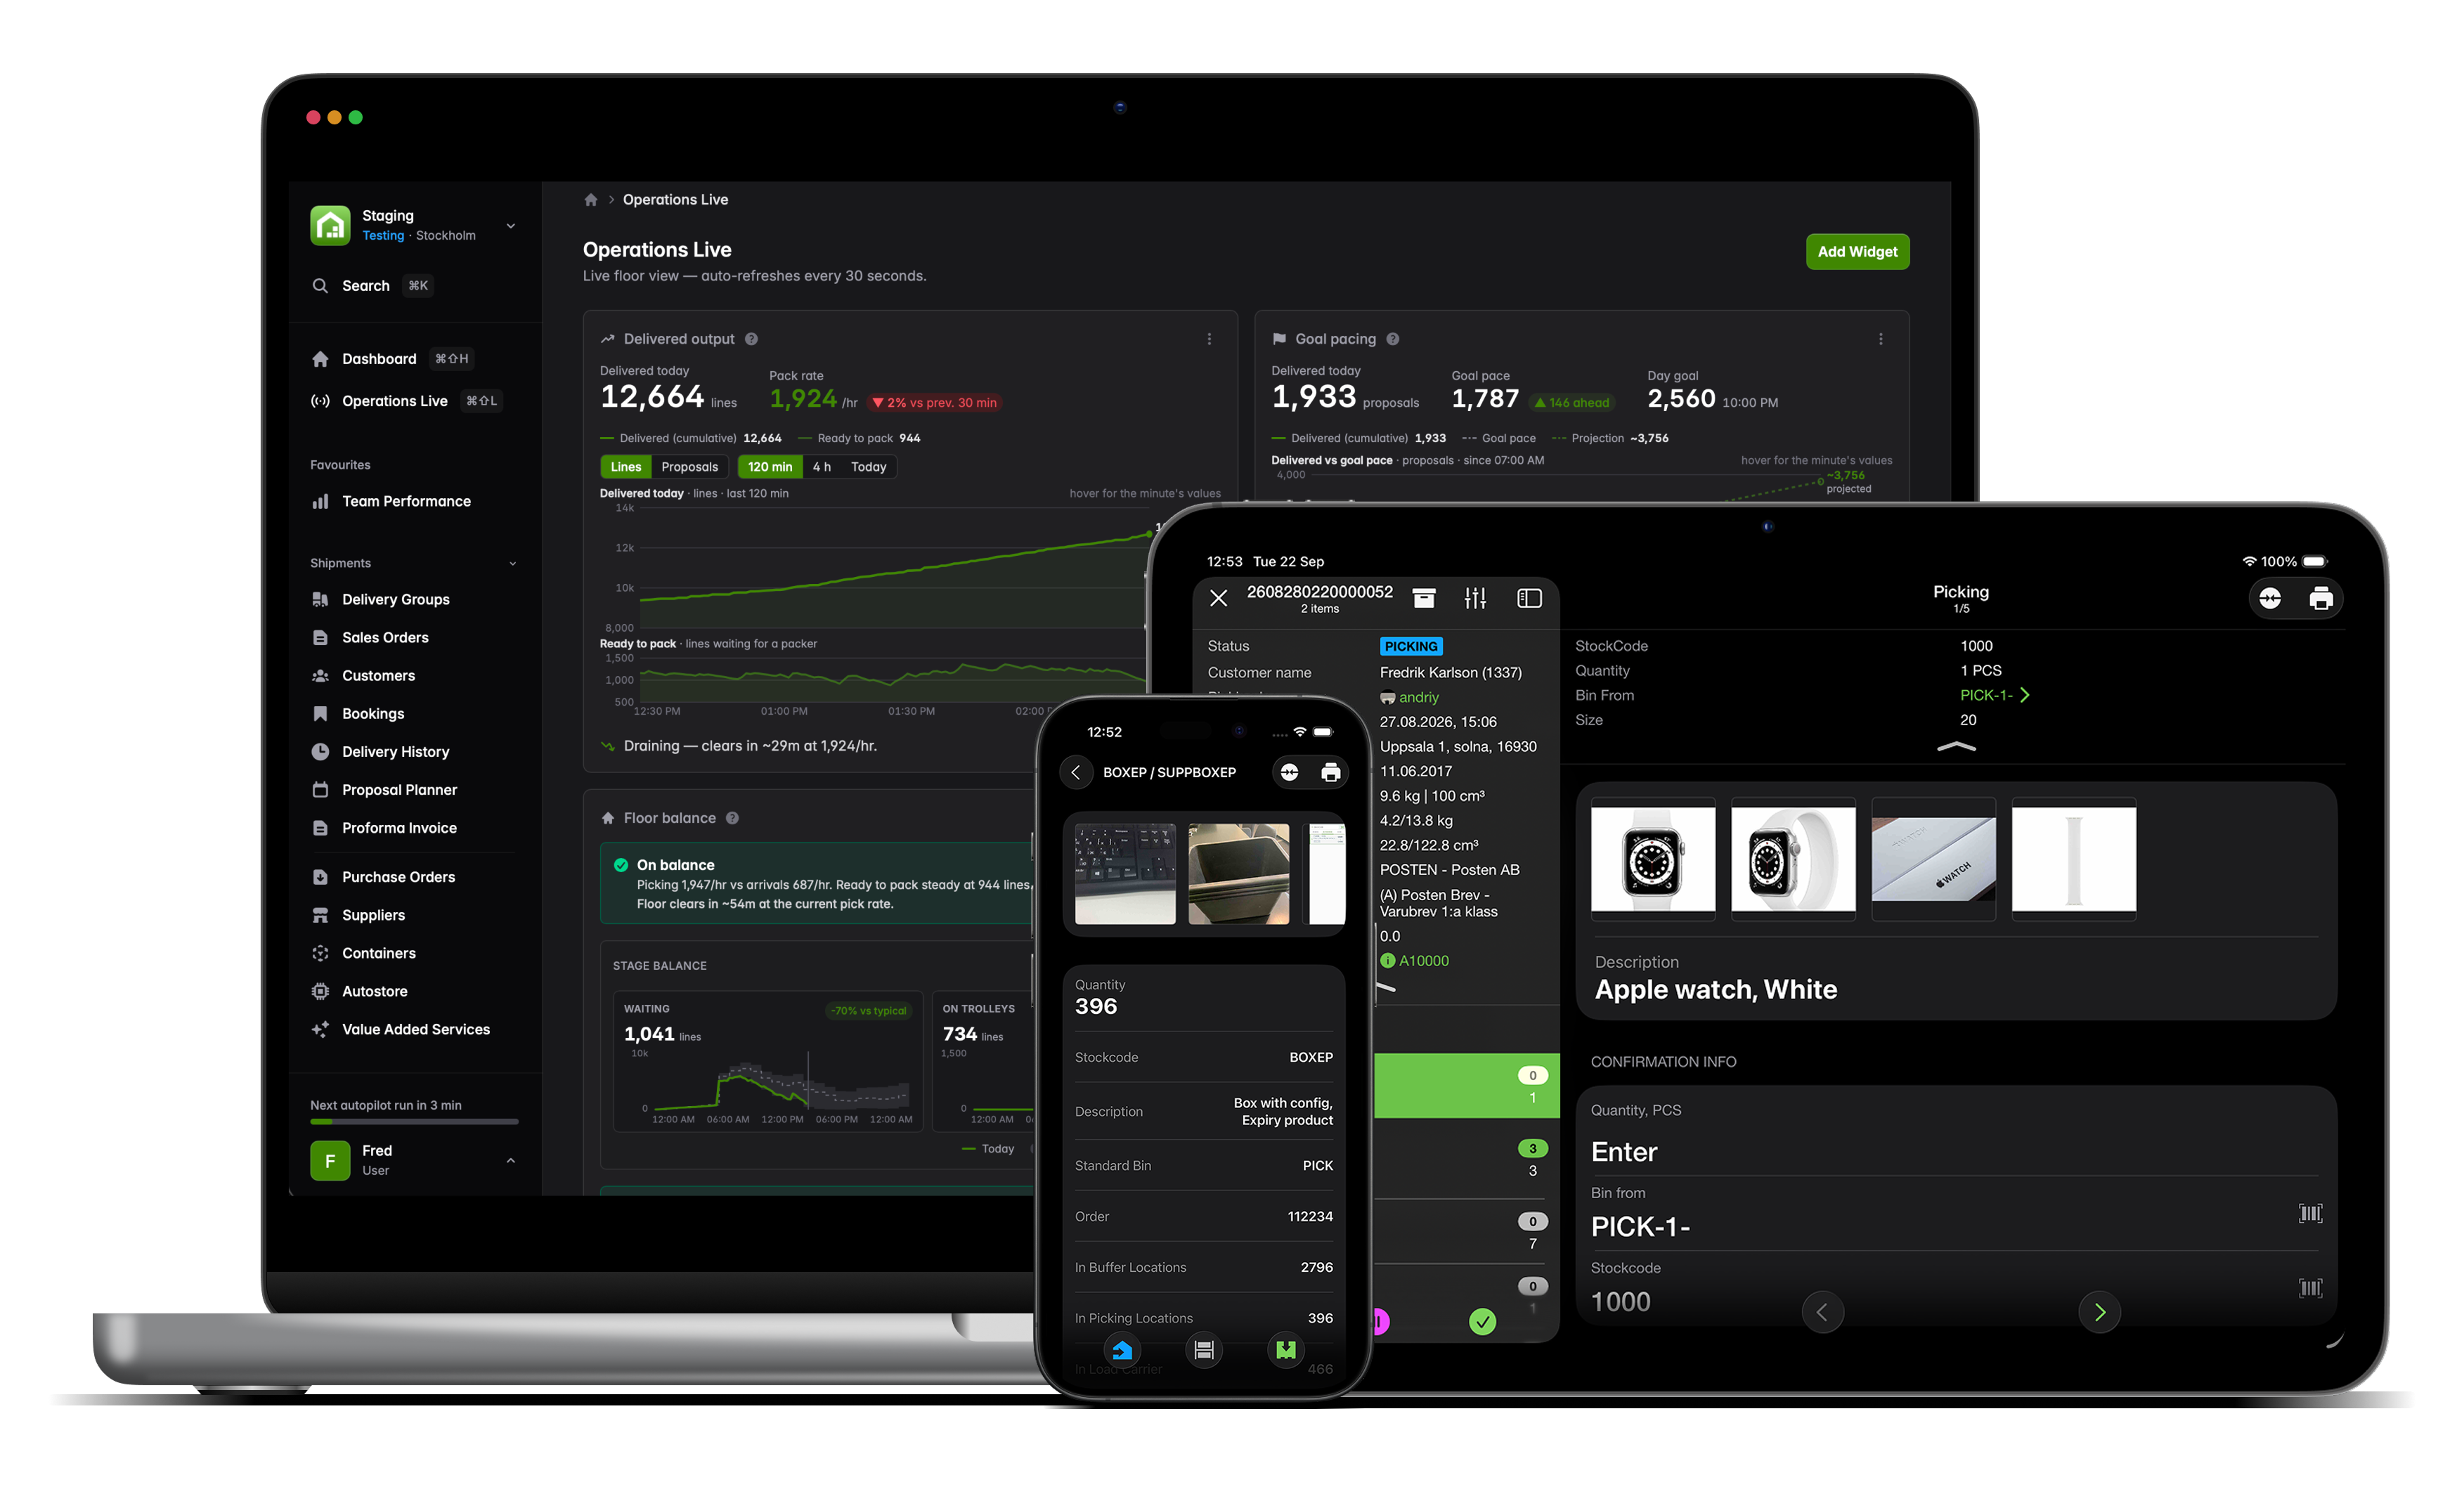
Mobile tablet laptop bitlog 11
5–25 min
Measured failover RTO across 11 tracked incidents.
Near-zero RPO
from continuous transaction-log replication, with 30-day point-in-time restore.
TLS 1.3 Encryption
in transit on every public and internal connection.
1 DB per tenant
A dedicated Azure SQL database per customer. No shared data plane.

The essentials at a glance

Three questions decide most WMS evaluations: is our data isolated, will it stay up, and will it connect to what we already run. Here's the short version.

 
What you're evaluating
How Bitlog handles it
Isolation One dedicated Azure SQL database per tenant. No shared data plane, so one tenant's credentials cannot reach another's data.
Encryption TLS 1.3 in transit on all connections. Azure SQL TDE at rest, with keys managed in Azure Key Vault.
Failover RTO     ~5–25 min on failover. ~60–90 min for a full environment rebuild from Terraform. Measured, not estimated.
RPO Near-zero. Continuous transaction-log replication, with point-in-time restore to any second for up to 30 days.
Authentication SSO through your own identity provider, including Microsoft Entra ID.
Certifications GDPR DPA in place. Azure infrastructure holds ISO 27001 and SOC 2 (maintained by Microsoft). Bitlog's own ISO 27001 is in progress, will be complete by end of 2026.


Want the full picture?

The complete Security, Resilience and Operations Brief, including the risk matrix, incident summaries, and restore-test records, is available on request.

Security and compliance

All data uses TLS 1.3 in transit and Azure SQL Transparent Data Encryption at rest. Public endpoints sit behind Cloudflare WAF with full DDoS protection, backed by Azure Traffic Manager failover, a path that was exercised for real during the Cloudflare global outage in November 2025.

A GDPR DPA is in place with every tenant. The Azure infrastructure Bitlog runs on holds ISO 27001 and SOC 2, maintained by Microsoft. Bitlog's own ISO 27001 is in progress. The full security brief, ISMS, and risk matrix are available under NDA.
Parcello having a shiny warehouse
Customer stories
format_quote
With Bitlog WMS we're seeing a 40% increase in operational efficiency and a 25% reduction in staffing costs.
Magnus Olsson
Magnus Olsson Head of Logistics, Care of Carl
format_quote
It's incredibly easy for us to train new colleagues and get them operational.
Hampus Bergdahl
Hampus Bergdahl Data Engineer, Nordic Nest
format_quote
When we started working with Bitlog WMS, we set a goal of 100 order lines picked per hour within a year. We achieved that in four months.
Anette Mühlbach
Anette Mühlbach Chief Supply Chain Officer, Apohem

Cloud-native on Azure, isolated per tenant

Bitlog runs entirely on Microsoft Azure: a private Kubernetes cluster at the compute layer, and a dedicated Azure SQL database per tenant at the data layer. There's no shared table, no shared schema, and no path by which one tenant's data can reach another's.

If a compromise is ever confirmed, Bitlog doesn't restore. It destroys the environment and rebuilds it from infrastructure-as-code in a clean state. No servers for you to manage, no patching cycles, no infrastructure budget beyond the subscription.
Firefly_Gemini Flash_Låt den animerade figuren hålla fram ett gammalt modem från 90-talet. Figuren ska se  766177 - Edited

Availability and recovery, measured not estimated

The RTO and RPO figures on this page come from real measurements across eleven tracked incidents, not architecture estimates. Mean resolution time for SLA-impacting incidents was roughly 30 minutes. Full incident summaries are available under NDA.

check_alert

Failover scenario

If the primary cluster becomes unavailable, Azure Traffic Manager re-routes traffic to the secondary endpoint within DNS TTL (up to 10 minutes). Total end-to-end RTO: roughly 5 to 25 minutes.

build

Full rebuild scenario

In a catastrophic loss or a confirmed compromise, the environment is destroyed and re-provisioned from Terraform and verified source code. Total end-to-end RTO: roughly 60 to 90 minutes.

backup

Recovery point

Azure SQL runs continuous transaction-log replication, not scheduled backups. Point-in-time restore is available to any second within 30 days, so RPO is near-zero.

AI now, agent-ready next

Where the AI is real in Bitlog WMS

Plenty of WMS vendors will tell you AI runs the warehouse. We won't, because it doesn't. Here's exactly what's in Bitlog WMS and what's still on the roadmap, so you can evaluate the claim instead of the marketing.

check_alert

Live now: Anonymized AI coaching insights

Each picker sees today vs. goal, their trend, and the anonymized team average. Names never leave Bitlog. (Powered by Claude)

build

Live now: In app assistant

Ask Parcello our in app assistant inside Operations Live, for deeper reads on what's happening on the floor. (Powered by Claude)

backup

Roadmap: MCP endpoints for AI agents.

Read access comes first, so agents can query the warehouse, inventory, orders, and status, through a documented interface. Agent actions follow. To be launched end of 2026.

Not AI, and not pretending to be:

Autopilot plans the day, prioritizes orders, and re-optimizes the open backlog every few minutes. It's deterministic optimization, not a model, so it's auditable, repeatable, and it doesn't hallucinate. The AI assists and coaches. Your operations run on Bitlog's proven optimization engine.

It connects to the systems you already run

Bitlog is built API-first. Pre-built connectors cover Microsoft Business Central, Visma Business, and Visma Net, and Bitlog has a deep fit in the Business Central ecosystem (available on AppSource, MACC-eligible). Purpose-built connectors handle AutoStore via Element Logic, Kardex, and conveyor systems. ERP API credentials are stored encrypted per tenant in Azure App Configuration, backed by Azure Key Vault, and can be invalidated individually without touching any other tenant.

Your ERP stays the system of record. Bitlog runs the warehouse. For anything outside the pre-built list, the API-first architecture means custom connections are built against a documented, stable API surface.
parcello-integrations
Is Bitlog WMS cloud-native? expand_more

Yes. Bitlog runs entirely on Microsoft Azure, with a private Kubernetes cluster at the compute layer and a dedicated Azure SQL database per tenant at the data layer. There are no servers for you to manage, no patching cycles, and every customer is automatically upgraded to the same release.

How is our data kept separate from other customers? expand_more

Every customer has a dedicated Azure SQL database with database-contained users unique to that tenant. A credential from one database cannot authenticate against another, and no shared table or schema exists across tenants. Databases are reached through private endpoints from inside the Kubernetes cluster, so no tenant database is exposed to the public internet. Backups are per-tenant, geo-redundant, and fully independent.

What happens if Bitlog goes down during our peak season? expand_more

The architecture is built to absorb failures without service interruption. AKS runs a minimum of three pods per service with autoscaling and health checks, so a single node failure doesn't affect availability. If the primary cluster becomes unavailable, Azure Traffic Manager re-routes traffic to a secondary endpoint within roughly 10 minutes. In a worst-case full rebuild, the environment is re-provisioned from infrastructure-as-code in 60 to 90 minutes. These are measured figures, not estimates.

What integrations does Bitlog WMS support? expand_more

Bitlog is built API-first, so integration is the default rather than the exception. Pre-built connectors cover Microsoft Business Central, Visma Business, and Visma Net, with no custom API development required on your side. ERP credentials are stored encrypted per tenant in Azure App Configuration, backed by Azure Key Vault, and can be invalidated individually without affecting any other tenant. For systems outside the pre-built list, the open API surface supports custom integrations.

Is Bitlog ISO 27001 certified? expand_more

Not yet: Bitlog's own ISO 27001 is in progress, and set to be done before end of 2026. The Azure infrastructure Bitlog runs on already holds ISO 27001 and SOC 2, maintained by Microsoft. A GDPR DPA is in place with every tenant, and the full ISMS and risk matrix are available under NDA.

Does Bitlog support MCP for AI agents? expand_more

Not yet. MCP is on the roadmap for around the end of 2026, with read access first, so agents can query warehouse data (inventory, orders, status) through a documented interface, and agent actions to follow. We'd rather tell you it's coming than claim it ships today.

Who is responsible for security, Bitlog or us? expand_more

Responsibility is split clearly. Bitlog owns the infrastructure, application code, tenant databases, OS patching, and container security. You own your end-user accounts and offboarding, the content and quality of your tenant data, integration credentials on your side, and the host machines running any optional on-prem print clients. Bitlog provides the mechanisms and controls; you operate them for your own users. A full shared-responsibility matrix is in the Security, Resilience and Operations Brief.

Want to go deeper on the technical setup?

Book a session with Bitlog's technical team. They'll walk through the integration architecture, answer your security and compliance questions, and confirm what implementation looks like for your specific stack. Implementation is about five weeks of actual project work, run over five to twelve weeks at a pace that fits your operations.

Different roles ask different questions

Your ops lead, your CEO, and your CFO each weigh a different thing. Here's the page written for each.